
- Compliance solutions · NIS2
Navigate NIS2 with confidence.
The EU’s NIS2 Directive raises the bar for risk management and incident reporting. GFI products help you address key requirements, starting with vulnerability and patch management.
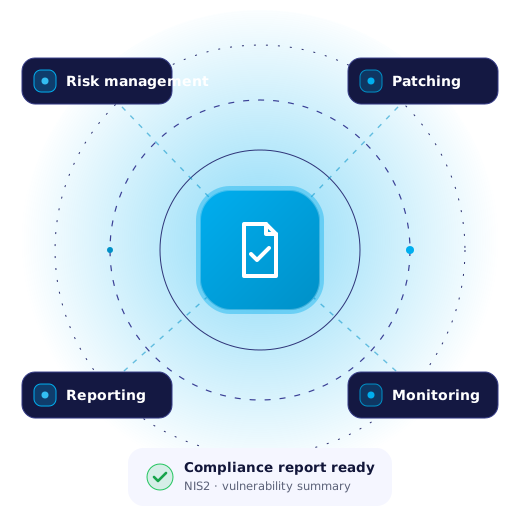
NIS2 Directive
What is the NIS2 Directive?
NIS2 is a framework to strengthen cybersecurity across EU member states. It covers organizations vital to the European economy and society, and requires risk management and incident reporting measures.
Compliance
Key compliance requirements.
Risk management
Network and supply chain security, access control, encryption and incident management.
Corporate accountability
Management must be trained on, oversee and approve cybersecurity measures.
Reporting obligations
Prompt incident reporting, including a 24-hour early warning.
Business continuity
Recovery, emergency procedures and a crisis response team.
Timeline
From NIS to NIS2.
A stronger directive
NIS2 revamps the original directive to address uneven implementation across member states.
Essential or important
A simpler classification of entities into two groups.
Wider reach
New sectors such as wastewater, food and space, covering medium and large companies.
GFI solutions for NIS2
Products that support your NIS2 program.
GFI LanGuard AI
NIS2 highlights vulnerability assessment and patch management. Discover devices, find missing patches and known vulnerabilities, deploy patches centrally, and report on NIS2, PCI DSS, HIPAA, ISO 27001 and SOX.
GFI ClearView AI
Monitor applications, users and bandwidth in real time, spot rogue applications, and keep up to two years of data for compliance reporting.
Start your NIS2 readiness with GFI.
See how GFI LanGuard AI and GFI ClearView AI support vulnerability management, monitoring and reporting.