GFI LanGuard for MSPs uses pay-per-scan monthly billing, so you can offer vulnerability and patch management services and only pay for the scans you run.
Regulations like NIS2 in Europe, CRF in Saudi Arabia and Essential Eight in Australia require vulnerability assessment and patch management. Adding them to your managed services helps clients build a strong security posture.
Flexibility
Pay-per-scan lets you serve clients with very different needs.
Comprehensive
From vulnerability identification to patching and hardware and software audits.
Cost-effective
Pay only for the scans you run and protect your margins.
Reliable
A trusted, established solution that delivers consistent results.
Deployment options
Deploy the way each client needs.
Deploy once on a mobile device
Ideal for clients who need occasional or periodic audits, such as a yearly cybersecurity audit.
Deploy on each customer’s machine
For clients who need one or more audits every month.
What you can offer
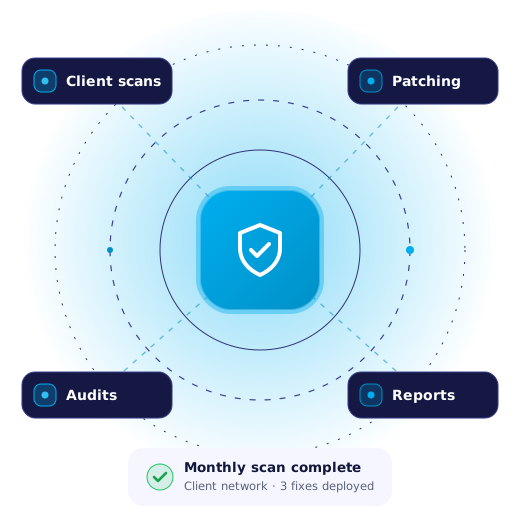
A complete vulnerability management service.
Vulnerability assessment
Identify and categorize known vulnerabilities, with recommended fixes.
Patch deployment
Patch operating systems, third-party apps and web browsers.
Hardware and software audits
See devices, installed software, open ports and shares.
Network device scanning
Cover switches, routers, access points, printers and mobiles.
Compliance reporting
Reports that support PCI DSS, HIPAA and other standards.
Web-based reporting
A secure web console, even across multiple sites.
ONE CONSOLE
Manage every client from one console.
GFI AppManager AI brings all your GFI products and customer accounts into one cloud console.