
NIS2 DIRECTIVE
What is the NIS2 Directive?
The NIS2 Directive is a robust framework instituted to bolster the cybersecurity posture of EU member states, aiming at a resilient digital infrastructure capable of thwarting and managing cybersecurity incidents. This directive encompasses organizations vital to the European economy and society, mandating the implementation of risk management and incident reporting mechanisms.
COMPLIANCE
Key compliance requirements
Risk Management
Implementing measures such as enhanced network security, stronger supply chain security, better access control, encryption, and incident management to minimize cyber risks.
Corporate Accountability
Ensuring corporate management is trained on, oversees, and approves the entity’s cybersecurity measures to address cyber risks, with an understanding of the potential penalties including liability and temporary ban from management roles for breaches.
Reporting Obligations
Establishing processes for prompt reporting of significant security incidents, adhering to NIS2's specified notification deadlines like the 24-hour “early warning” requirement.
Business Continuity
Planning for business continuity during major cyber incidents, including system recovery, emergency procedures, and setting up a crisis response team.
TIMELINE
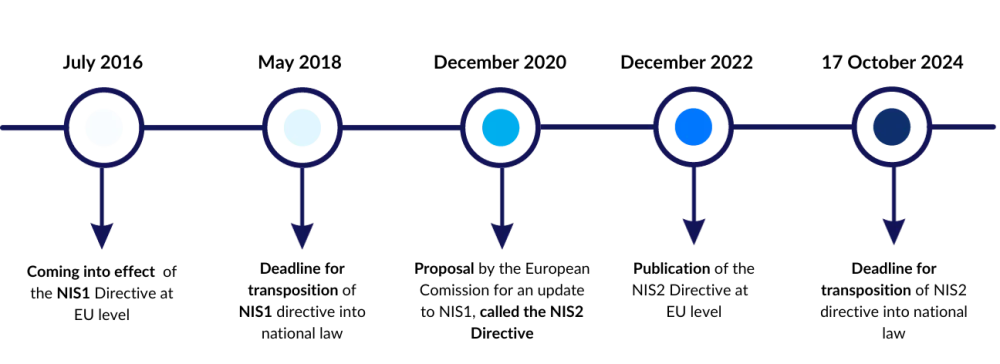
From NIS to NIS2
The initial NIS directive was a significant move towards enhancing cybersecurity within the EU, yet its execution led to a diverse implementation landscape across the member states. With the rise in cyber threats both in number and sophistication, the Commission revamped the directive into NIS2 to bolster security protocols, address supply chain security, simplify reporting obligations, and enforce stricter supervisory and enforcement measures. NIS2 simplifies entity classification into essential or important, extending its reach to include newer sectors like wastewater management, food, and space, encompassing all medium to large companies within these domains.
VULNERABILITY AND PATCH MANAGEMENT
Addressing Vulnerability and Patch Management
One of the key items that the NIS 2 directive highlights is the importance and requirement for vulnerability assessment and patch management. Article 6 in the directive talks about a vulnerability registry containing information about vulnerabilities, products or services it affects, along with the circumstances. It then expands to talk about the availability of patches and the requirements for when there are no available patches.
GFI LanGuard can assist organizations in complying with NIS2. For over a decade, GFI LanGuard has been enabling thousands of businesses across the globe to manage and maintain end-point protection across their network, providing visibility into all the elements in their network, helping assess where there may be potential vulnerabilities, and providing the ability to patch them. The patch management and network auditing solution is easy to use and easy to deploy.
For a more detailed overview, we encourage you to visit the GFI LanGuard page. You may also request a Live Demo for a product overview and to help answer any queries you might have.
GFI LANGUARD AI
Safeguard network security with GFI LanGuard AI
- Automatically discover all the elements in your network, including computers, laptops, mobile phones, tablets, printers, servers, virtual machines, routers, and switches.
- Scan your network for missing patches.
- Find gaps in common operating systems. Identify missing patches in web browsers and third-party software.
- Identify non-patch vulnerabilities by using a regularly updated list of 65,000+ known issues, as well as open ports and system information about users, shared directories, and services.
- Automatically deploy patches centrally, or deploy agents on individual machines.
- Run automated network security reports to help you demonstrate compliance with NIS2 and other requirements such as PCI DSS, HIPAA, ISO 27001/27002, and SOX.
GFI CLEARVIEW AI
Optimize network performance with GFI Clearview AI
- Automatically monitor health and performance of your entire network, including applications, users, and bandwidth consumption in real-time.
- Gain valuable insight with a unified dashboard for network and application performance.
- Identify bottlenecks and issues impacting application performance with comprehensive traffic analysis.
- Deploy instant monitoring with 1-second refresh time for immediate network visibility.
- Identify rogue applications that pose threats to your network before they can be exploited.
- Leverage built-in reporting tools for easy data analysis and compliance reporting, with up to two years of data retention.
BLOG
Learn more about NIS2
NIS2 Directive: Key Changes And Implications For IT infrastructure
The new EU NIS2 directive impacts several sectors and digital services, marking a new chapter in how we manage cybersecurity risks. Come along with us as we unravel the intricacies of NIS2, examine its implications on your IT infrastructure, and highlight how GFI Software’s solutions can streamline your journey into this new frontier of cybersecurity
What is NIS2? - A comprehensive overview of the new EU Cybersecurity directive
The European Union recently introduced the NI2 Directive, a comprehensive framework to strengthen the region’s defenses against digital threats. In this blog post, we’ll look at the essentials of NIS2, discuss key impacts, and requirements, and how GFI can help businesses navigate this new cybersecurity landscape.
Demystifying the NIS2 Cybersecurity Directive
Are you aware of the NIS2 cybersecurity directive recently introduced by the European Union? As a forward-thinking IT professional, it’s crucial to stay ahead of the curve and prepare for this groundbreaking regulation.
Already a GFI customer?