See how GFI KerioConnect® gives EU SMBs a data-sovereign alternative to Microsoft 365 and Google Workspace by running email on hardware you own in a jurisdiction you control, removing US CLOUD Act exposure while delivering the TLS, S/MIME, TOTP, audit logging, and Active Directory controls needed to evidence GDPR Article 32 and NIS2 compliance.
See how GFI KerioConnect® gives schools, academy trusts, and multi-site education organizations an on-premises email platform that keeps student data on their own infrastructure, out of US-cloud supply chains, with multi-domain trust management, staff/student separation, KCSIE audit logs, and full Outlook for staff on a budget that fits education funding.
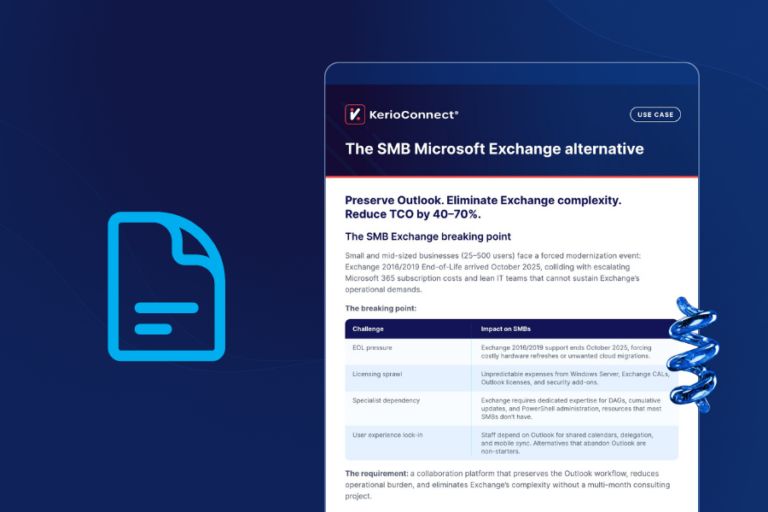
See how GFI KerioConnect® gives SMBs a seamless path away from Exchange 2016/2019 end-of-life, preserving the full Outlook experience while reducing total cost of ownership by 40–70%.
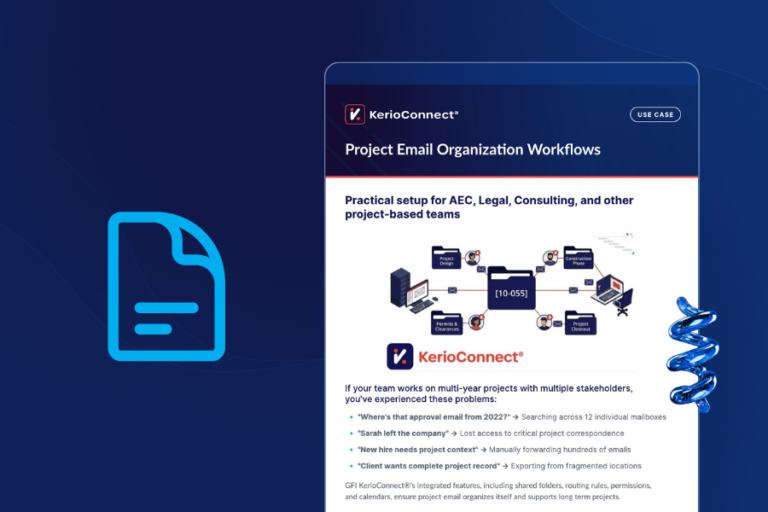
Discover how GFI KerioConnect®'s shared folders, routing rules, and permissions automatically keep project correspondence organized and accessible for AEC, legal, consulting, and other project-based teams.
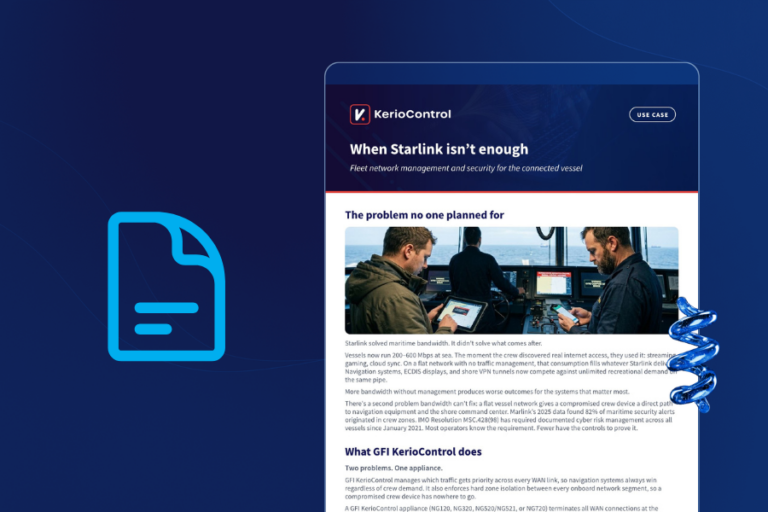
A use case showing how GFI KerioControl adds traffic prioritization, zone isolation, and IMO-compliant fleet management to vessels running Starlink, solving the network security and bandwidth management gaps that connectivity alone cannot fix.
GFI KerioControl's Shield Matrix AI closes the pre-signature threat gap for SMBs, using a global honeypot network to block known malicious IPs before any data exchange occurs, with no SOC required.
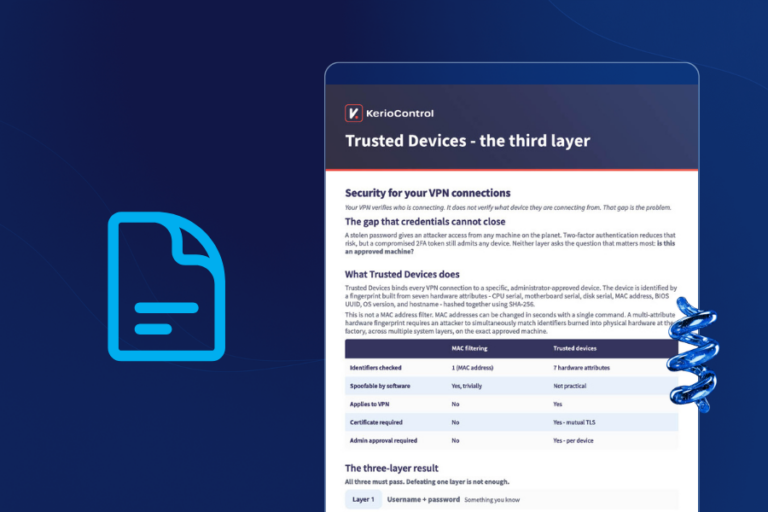
Covers the Trusted Devices feature in GFI KerioControl v10, which adds device verification as a third authentication layer on top of credentials and 2FA. Rather than a spoofable MAC address filter, it binds each VPN connection to a specific admin-approved machine using a SHA-256 fingerprint built from seven hardware attributes (CPU serial, motherboard serial, disk serial, MAC address, BIOS UUID, OS version, hostname), backed by mutual TLS certificates.